API Rate Limiting: Protecting Your System Without Frustrating Users
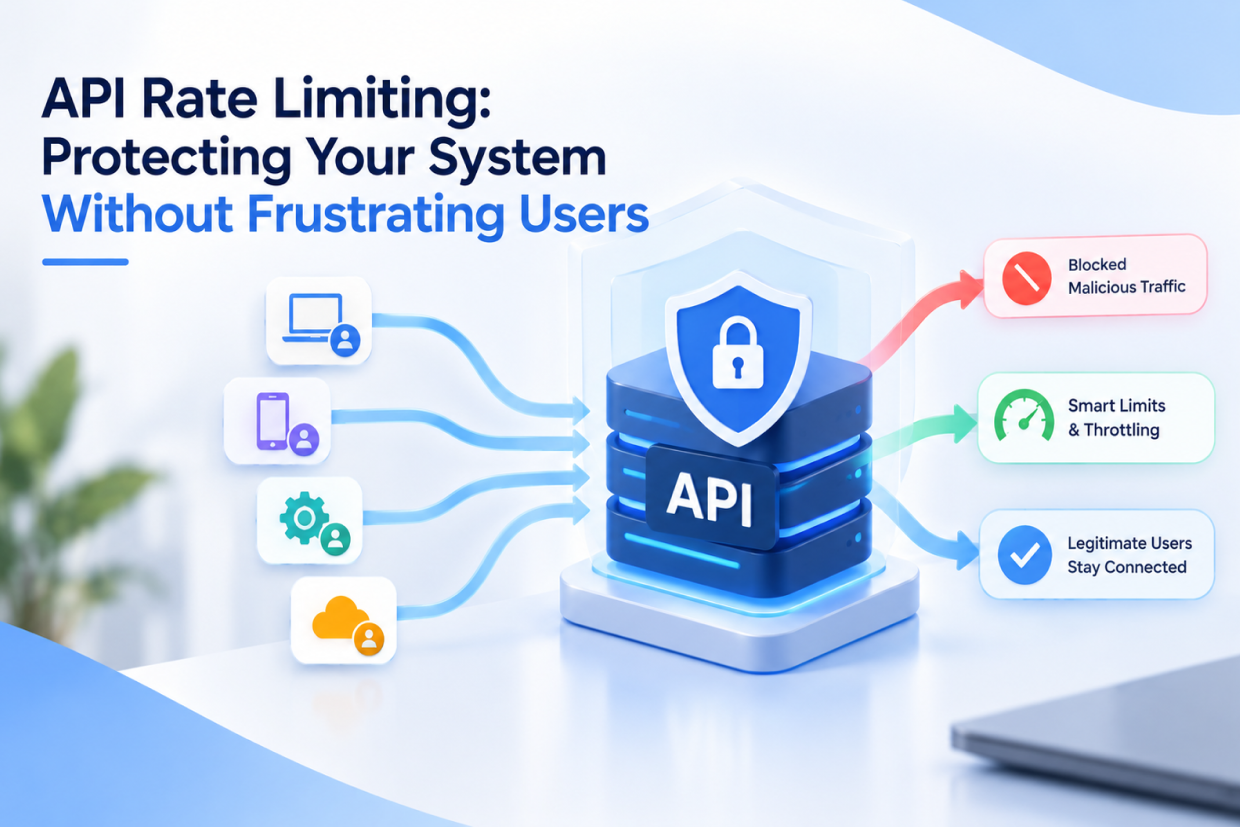
An API can be working perfectly until one client suddenly sends thousands of requests. Traffic increases, server resources are consumed, and other users may start experiencing slow responses or failures.
Rate limiting helps prevent this by controlling how many requests a client can make within a specific period. It protects APIs from accidental overload, abusive traffic, and poorly configured integrations.
A Flat Limit Can Frustrate Good Users
A common approach is to give every client the same request limit. This is simple to implement, but not every client uses the API in the same way.
A trusted business integration may need higher limits, while a public-facing client may require stricter controls. Treating both exactly the same can create unnecessary failures for legitimate users.
Rate Limits Should Match Usage
A better approach is to consider the client, request type, and usage pattern. Different customer tiers or API endpoints can have different limits based on their actual requirements.
| Situation | Suitable Approach |
|---|---|
| Trusted enterprise client | Higher request limit |
| Public API | Controlled standard limit |
| Sensitive endpoint | Stricter limit |
| Suspicious traffic | Temporary restriction |
This provides protection without treating every request as a potential threat.
Clear Errors Help Integrations Recover
When a client reaches its limit, simply returning an error is not enough. The API should clearly indicate that the limit has been reached and, where appropriate, provide information that helps the client determine when it can try again.
Good error handling allows applications to retry intelligently instead of repeatedly sending failed requests.
Rate Limiting Is More Than Traffic Control
Effective rate limiting protects the reliability of the entire platform.
It can prevent one client from consuming an unfair share of resources, reduce the impact of abusive traffic, and help maintain stable API performance during unexpected spikes.
The goal is not to block users. It is to protect the system while allowing legitimate traffic to continue.
Use Rate Limiting as Part of a Larger API Strategy
Rate limiting works best alongside authentication, monitoring, logging, caching, request validation, and clear API documentation.
Businesses should regularly review which clients are hitting limits and why. If legitimate integrations frequently reach the limit, the solution may be to improve the API or adjust the limits rather than simply blocking requests.
Good API rate limiting protects your infrastructure without becoming a barrier to the integrations that create value for your business.
What Sophisticated Abuse Looks Like Around a Simple Limit
A flat rate limit stops the obvious case — one client hammering an endpoint with requests. It does far less against a more deliberate pattern: distributing requests across many different accounts or IP addresses, each staying just under the limit individually, so the aggregate load on a specific endpoint is still substantial while no single client ever technically violates its own limit. Credential-stuffing attacks, where an attacker tests large numbers of stolen username-password pairs, are frequently spread this way specifically to stay under naive per-client limits.
Detecting this requires looking beyond individual client limits to patterns across all traffic — a sudden surge in requests to a login or authentication endpoint specifically, unusual geographic distribution for a client base that is normally concentrated in one region, or repeated failed-request patterns that look automated rather than human. Rate limiting is the first, necessary layer of protection. Catching genuinely sophisticated abuse also requires monitoring patterns that a single client's own request count could never reveal on its own.
At Vriksha Techno Solutions, API development and integration can include rate limiting, authentication, monitoring, validation, and scalable API architecture to keep systems reliable while supporting legitimate application traffic.
Ready to Build Your Next Digital Product?
Our experts will respond within 24 hours with a tailored approach for your project.